~/CyberSecurity Projects
# 23 entries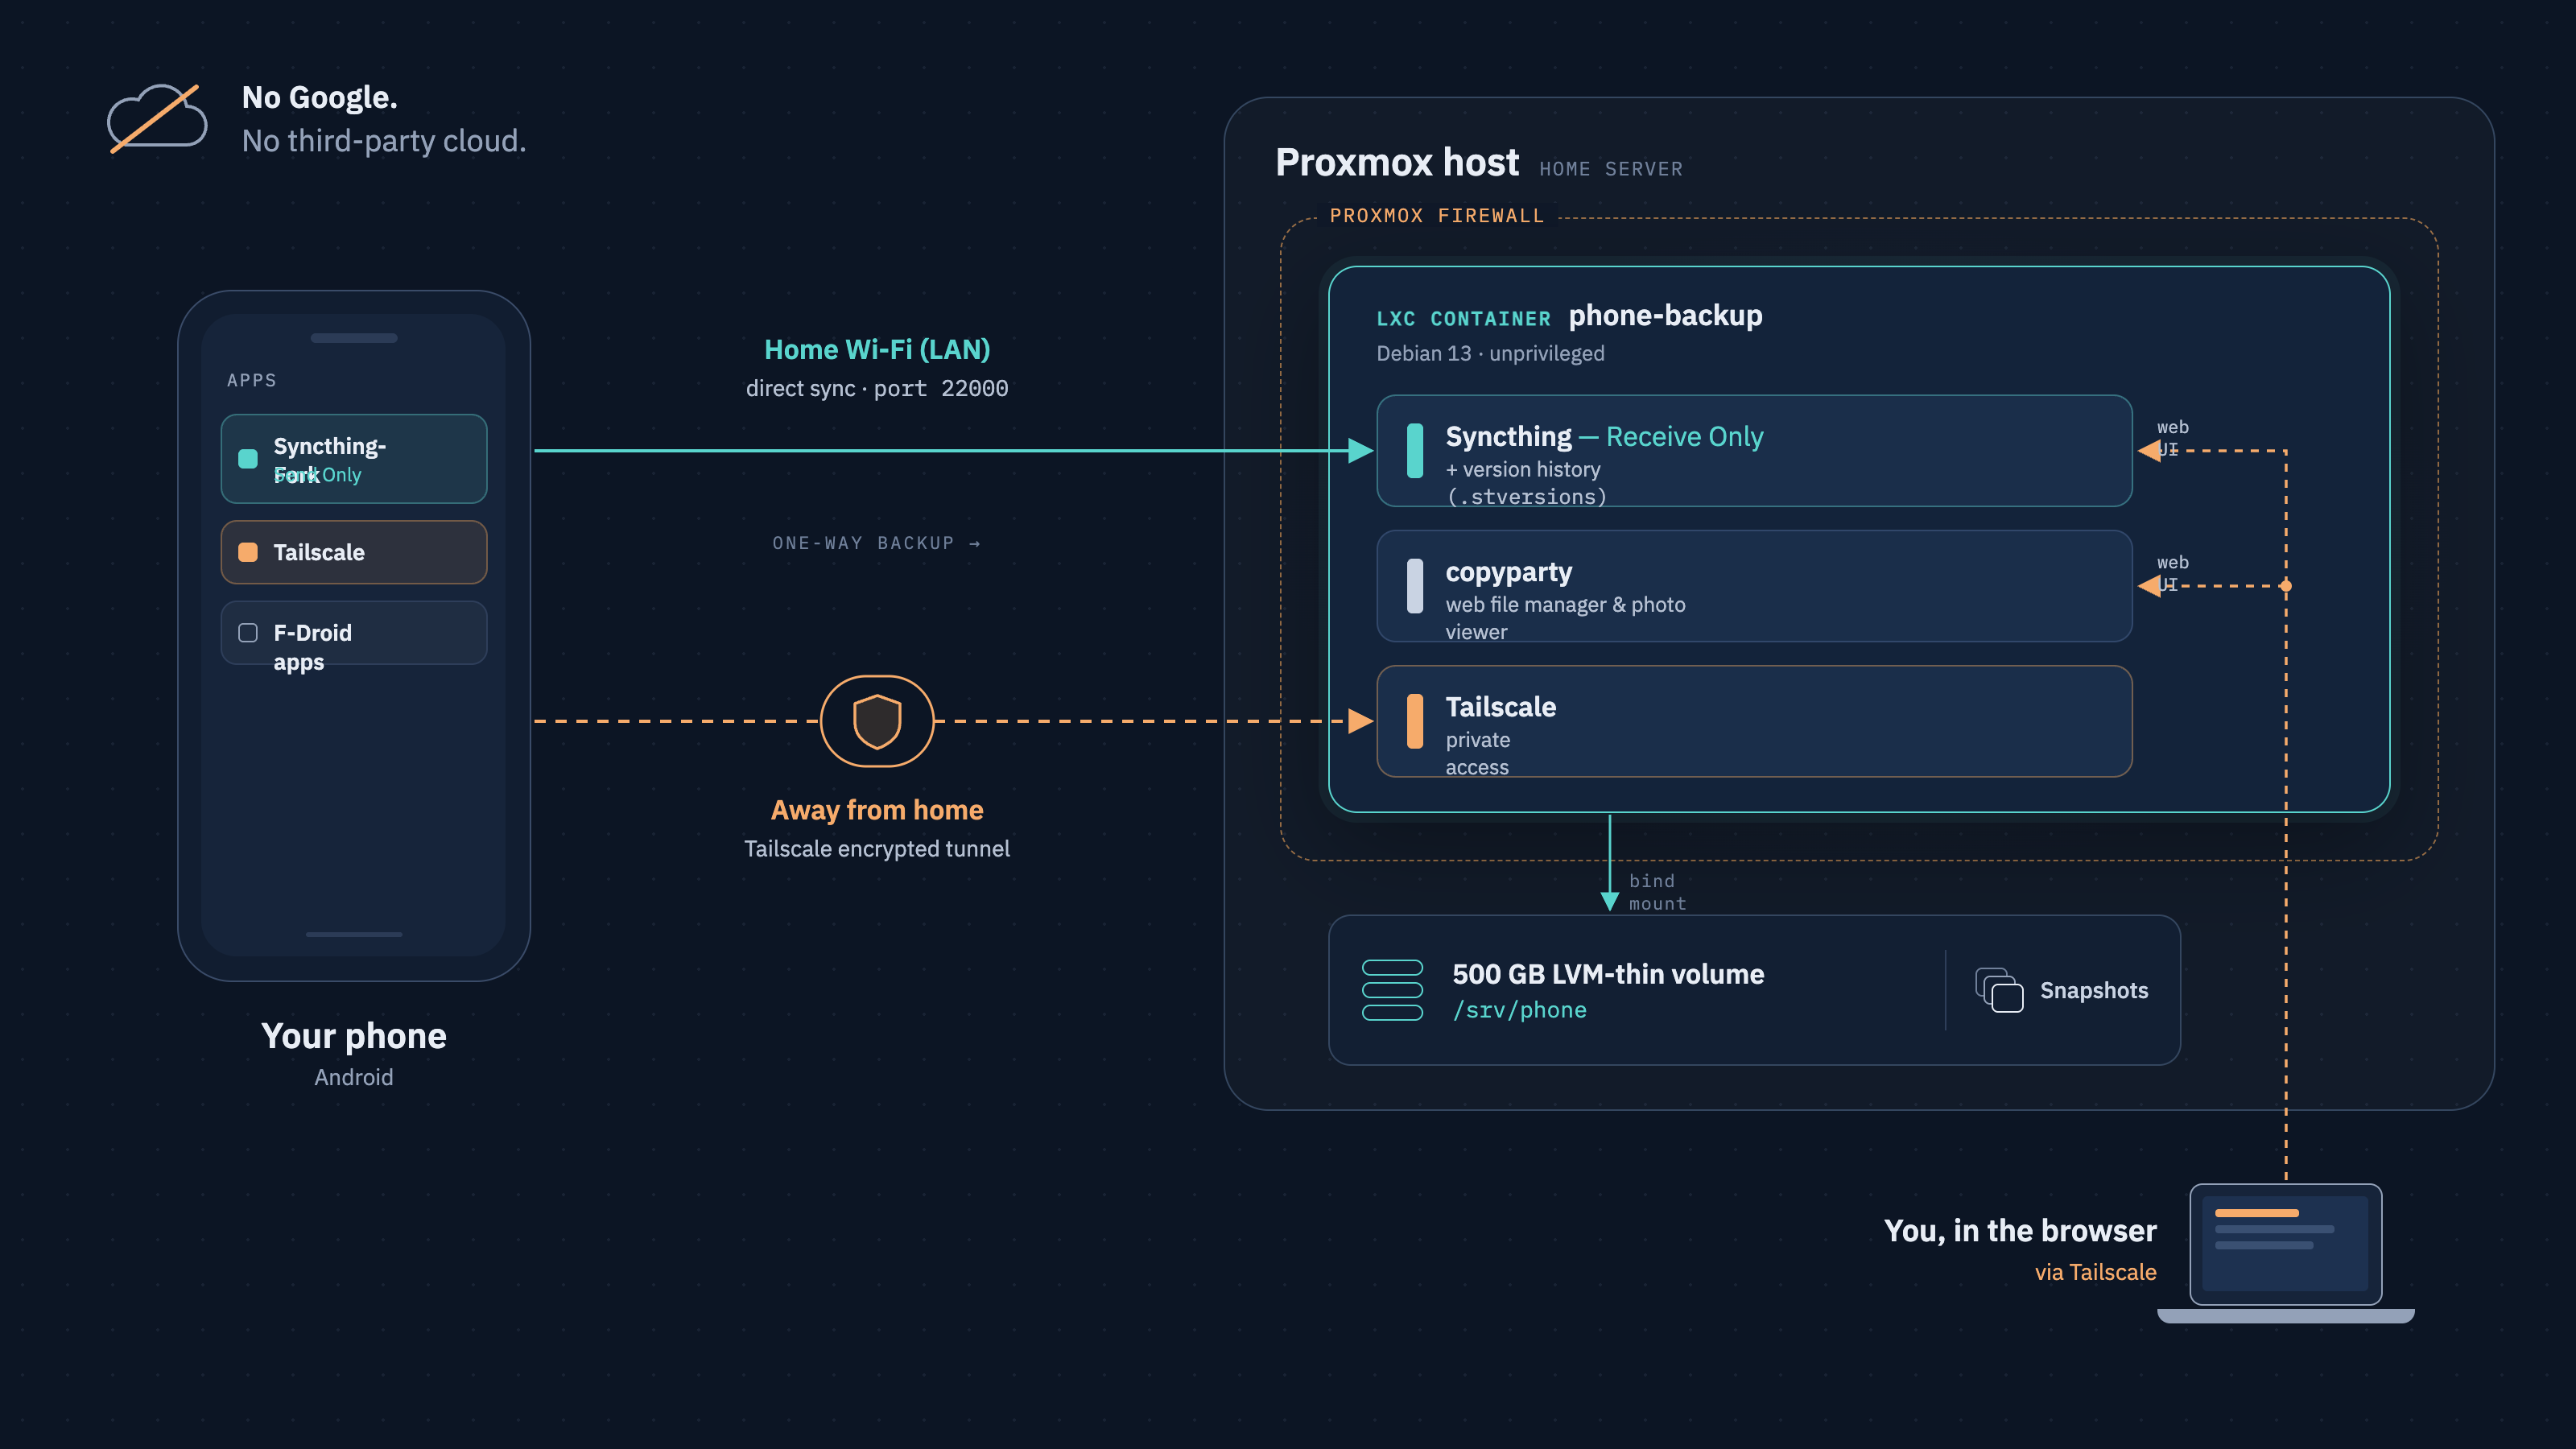
$ Self-Hosted, Google-Free Phone Backup on Proxmox
Built a private phone backup system in a hardened, unprivileged Debian 13 LXC on Proxmox with Syncthing and copyparty! Your data is yours alone. You deserve to choose where it’s stored, who it’s shared with, and how it travels over the internet.
$ Compliance Auditing & Automated Remediation with OpenSCAP
Audited a Rocky Linux 10 server against the CIS Level 1 benchmark with OpenSCAP, generated HTML compliance reports, and remediated only the failed rules through an auto-generated Ansible playbook, validated with a dry run and re-audited to measure before-and-after compliance.

$ File Integrity Monitoring (FIM) with Wazuh
Deployed Wazuh's syscheck for real-time file integrity monitoring over a Tailscale mesh, detecting unauthorized changes to critical files and directories through baseline comparison rather than signature matching.

$ Hardening macOS Against the CIS Benchmark with Wazuh
A hands-on walkthrough of reading, understanding, and manually remediating CIS benchmark findings on macOS. No MDM required.

$ Centralized Security with Wazuh, Proxmox, and Tailscale
Deploying a Security Operations Center, monitoring my own infrastructure: a bare-metal hypervisor with Proxmox and cloud computing.
$ Monitoring as a Security Control: UpTime Kuma
Architected a secure external uptime monitoring pipeline using self-hosted Uptime Kuma on Proxmox, leveraging SQLite for minimal attack surface and out-of-band Telegram alerts to ensure availability detection independent of monitored infrastructure.
$ Resilient Bulk Email: Subdomain Isolation with MailerLite
Architected a bulk email infrastructure using subdomain isolation to protect primary domain reputation, with manually configured SPF, DKIM, and DMARC for full authentication control.
$ Building a Technical Documentation Site with Zensical
Self-hosted technical documentation built with Zensical, a fast static docs generator full data ownership.
$ Penetration Testing: Validating My Infrastructure Against SQL Injection with Exegol & SQLMap
Offensive security simulation with SQL injection detection and vulnerability validation.
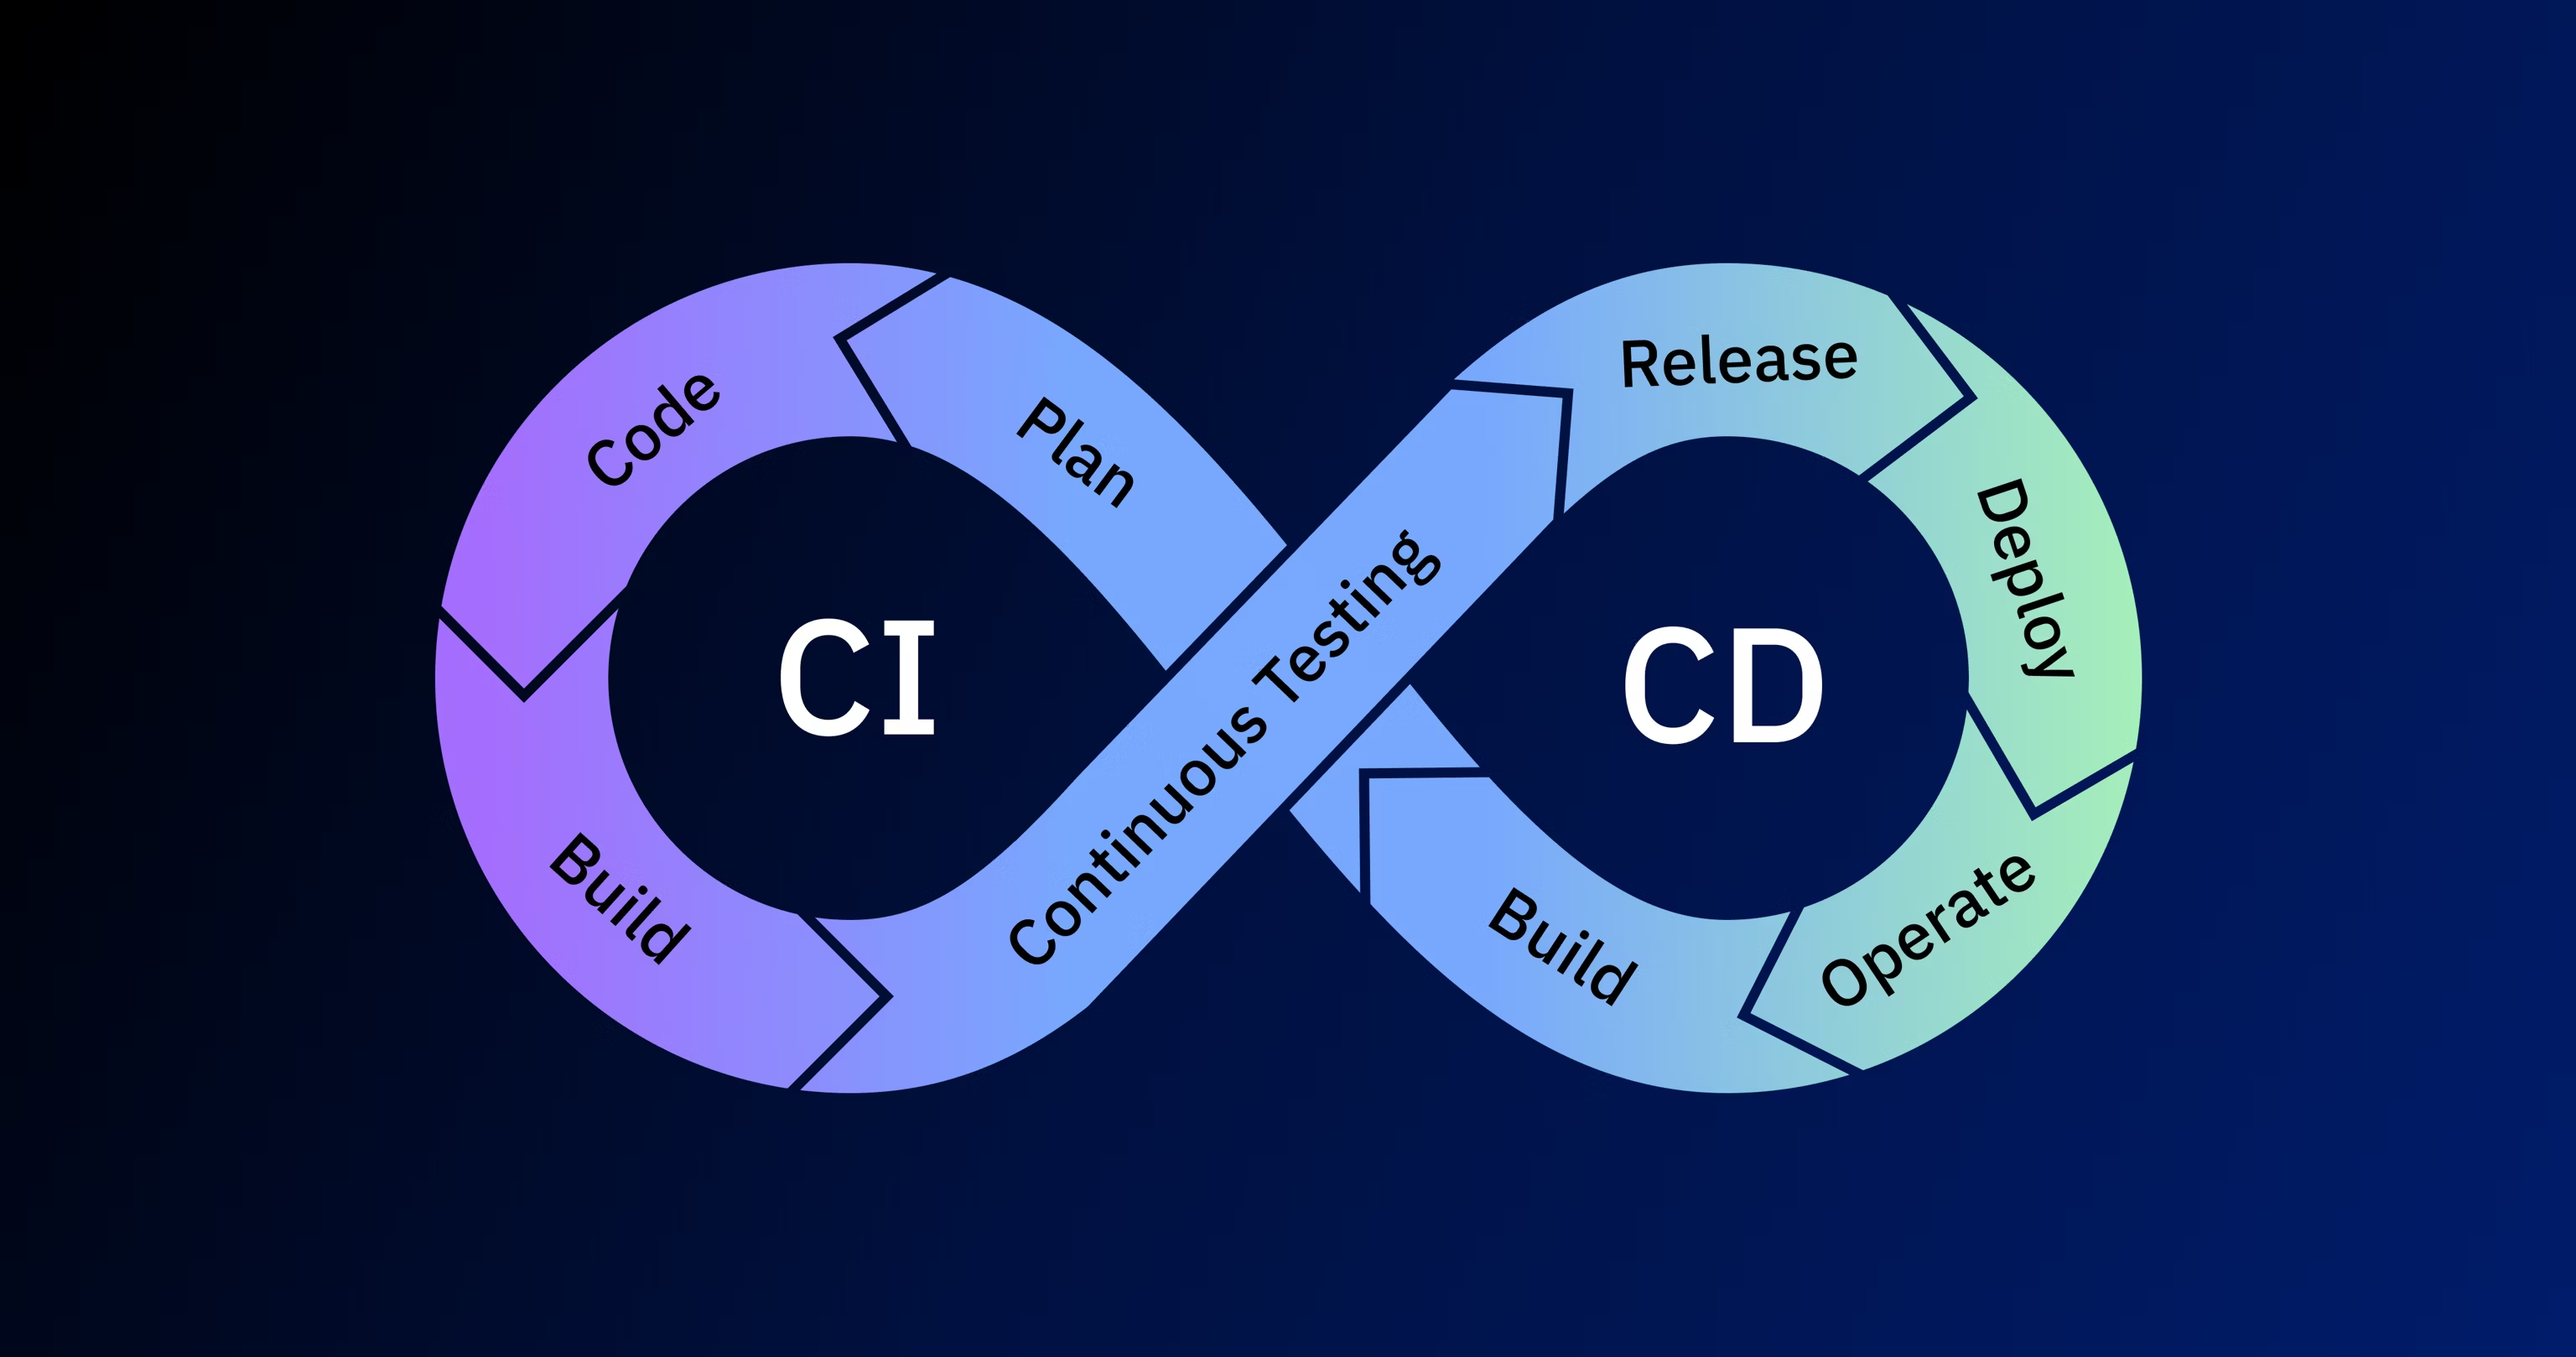
$ DevSecOps: Automating Secure Deployments with GitHub Actions
Automated security gates with secure deployment and CI/CD integration.